Asos appears to have been hacked, with customers sent a bizarre, threatening notification.
Users of the app received a message on Tuesday morning indicating that the company’s systems had been compromised.
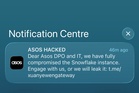
“Dear Asos DPO and IT, we have fully compromised the Snowflake instance,” the message, apparently written by the cyber attackers, reads. “Engage with us, or we will leak it,” it continues, before linking out to a Telegram chat.
DPO refers to the data protection officer, the appointed person in a company who takes responsibility for safeguarding customers’ information. Snowflake is an online data platform used by a wide array of companies.
Asos did not immediately respond to a request for comment. It is also yet to post about the notification or possible cyber attack on its social media accounts.
It is not clear how many customers the notification was sent to. But it appears to have been delivered to at least a large number of the app’s customers.
Asos says that it has 17 million customers each year, in more than 150 countries. That was down slightly on last year, when 19.7 million people shopped on the site.
It reported revenues of £2.5 billion in 2025, down from £2.9 billion the year before. That led to an operating loss of £212 million last year.
Key Points
- Asos finally addresses 'hacked' alert
- What should customers do now?
- Don't interact with notification, expert urges customers
- What is Snowflake?
- Asos share price plunges
Asos's statement doesn't help share price – but doesn't harm it either
15:56 , Andrew GriffinThe stock market seems neither perturbed nor buoyed by Asos’s statement. The share price is still down around 11 per cent over the day – it fell soon after the notification came out, and has been stuck there ever since.
Asos finally responds to hack
15:37 , Andrew GriffinMore than five hours after the notification was sent, Asos has finally responded. It says that personal information may have been accessed in the cyber attack.
“ASOS can confirm that, at around 10am today, an unauthorised customer notification was sent to ASOS customers,” Asos said.
“We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers.
“We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities.
“Basic personal information including name and contact details may have been accessed. We do not believe that payment-card information or account passwords, were impacted.
“Our website and app are operating as normal, with no current disruption to any aspects of our operations.
“Customer trust is incredibly important to us, and if the situation changes an update will be provided as appropriate.
“The Company has cyber security insurance with a large global provider, including business continuity insurance. It is too early to quantify any potential impact on trading.”
Push notifications are one of the 'hardest-working channels' – but could this undermine trust?
15:08 , Andrew GriffinThe website might still be up – but it is important that users continue to trust push notifications, said one marketing expert, and that could be undermined by the worrying update this morning.
“Asos’s website never went down, but the commercial damage can start the moment customers lose trust in the messages coming through its own channels. People let a brand onto their phone because they trust it. Once that channel has been used to threaten them, they may start questioning genuine messages too,” said Marty Bauer, ecommerce expert at marketing company Omnisend.
“Push notifications are one of the hardest-working channels retailers have. Across brands using Omnisend, push automations had a 22.9% conversion rate last year. If customers now switch notifications off or stop engaging with them, that could have a direct impact on repeat sales.
“The first practical step is to pause any automated promotional sends. A discount arriving before an explanation of that notification risks making customers feel their concerns are being ignored.
“With Black Friday approaching, Asos will want existing customers to feel comfortable buying again. If shoppers disengage from push notifications and email now, that is revenue the brand may find difficult to win back.”
Asos chatbot says company is 'currently investigating'
14:15 , Anthony CuthbertsonThere is still no official comment from Asos about the apparent hack, but the online chatbot on the company’s website has said that the incident is under investigation.
The bot said: “We’re aware of the notification and are currently investigating. We son’t have any further information to share at this stage, but we’ll provide an update as soon as we know more.”
What is happening at Asos?
13:36 , Anthony CuthbertsonWe’ve heard from Matt Hull, VP of Cyber Intelligence and Response at the cyber security company NCC Group, about what is happening at Asos and what the company should be doing next:
Matt Hull, VP of Cyber Intelligence and Response at NCC GroupWhile the nature and extent of the reported incident remain unclear, the immediate priority for any organisation responding to a suspected cyber attack is containment. Before a business can return to normal operations, it needs to be confident that the attacker’s access has been identified and cut off.
Incident responders need to establish how the attacker gained access, which accounts and systems may have been compromised, what they were able to reach and whether they have other routes back into the environment. The decision to keep systems running or take them offline should be guided by the forensic evidence.
Asos are likely to be juggling a huge amount behind the scenes. The important thing is to communicate to customers and stakeholders what they know when they know it, be clear about what is still uncertain, and avoid leaving customers or other stakeholders guessing. Cyber incidents are rarely resolved in hours. Understanding the full scope of an attack, containing the threat and making sure an attacker cannot return can take days or weeks. Recovery comes once those stages have been worked through and the organisation can be confident that it is secure enough to operate normally again.
Asos still yet to publicly acknowledge threatening notification
12:54 , Andrew GriffinAfter this morning’s notification, seemingly sent by hackers, Asos has remained silent on the attack. Its website and app appear to still be operating as normal, and the company is yet to make any public statement about the incident.
Asos share price plunge seems to stabilise
12:50 , Andrew GriffinAsos’s valuation has been plunging since around 10am local UK time, just after the notification hit users’ phones. It fell for about an hour and then seemed to stabilise – and the initial impact of the cyber attack now seems to have been digested, with the share price down around 13 per cent since this morning.
Cyber attack could endanger customers for 'months to come'
12:49 , Andrew GriffinWe still don’t know what data – if any – was compromised in the hack. But if the attackers got access to customers’ information, then the effects of the hack could last for “months”, a cyber security expert has warned.
“If customer information has been exposed, criminals could turn it into convincing scams for months to come. A fake delivery charge or refund message can feel credible when it includes your personal details; one visit to a fraudulent payment page could then hand criminals your card details,” said Gavin Millard, vice president of product at security firm Tenable.
“Customers should be wary of unexpected messages asking for payment or personal information, and check any request through the retailer’s official website or app. Businesses need to establish what has been accessed and communicate clearly, so customers know what to watch for.”
Who are the hackers?
12:08 , Andrew GriffinIn the notification sent to users, hackers did not identify themselves. But they included a link to a Telegram chat, created today, that appears to identify them as “Xuanye Group”.
That is not a well-known hacking group and there is no indication they have been involved in any cyber attacks in the past.
The group did not make any specific demand in the channel, to Asos or anyone else, despite the suggestion in the push notification that it was threatening the company. And it also claimed that financial data had not been affected – though of course there is no particular reason to trust that assurance.
As below, experts really urge users not to click through on that link, the notification, or anything else that might come from the hackers.
What should customers do now?
11:47 , Andrew GriffinHere’s some more advice from experts about what to do if you’ve received the notification, or are generally concerned about the possible hack on Asos. The short version is: we don’t really know enough about what happened to be specific, but don’t panic, and there are important ways to be careful that will help you either way.
“Getting a message like that from an app you trust is genuinely unsettling. Most people think of a hack as something that happens out of sight, so seeing a threat land on your own phone makes it feel much more personal. It's completely understandable that people are worried, but the most important thing right now is not to panic. At times like this, panic can make matters much worse,” said Pete Membrey, chief research officer at ExpressVPN.
"The truth is we don't know much yet, and 'don't know' means don't know. A knee-jerk reaction could be exactly the wrong thing to do. What people can do is some simple due diligence. Don't tap on the notification or follow the link in it. Go to the ASOS website directly, by typing in the address yourself rather than through an email or the app, and reset your password. If the attackers have compromised that side of things, they may already have your old password, and if they're still inside they could potentially see the new one too. But it's a quick, simple step that should, in general, draw a line under it.
"What's more critical is everywhere else you've used that password. Everyone knows they shouldn't reuse passwords, but it happens. Maybe you needed to set something up in a hurry, or there's an old account you never got around to updating. If attackers have your password, you can guarantee they'll try it in every lock they can find. Without a password manager, that could take them about five minutes.
"So take this as a wake-up call to finally get a password manager and start updating your passwords. If nothing was leaked, great, you've still massively upgraded your security against future attacks. And if it was, you've slammed the door shut before anyone could take advantage. Either way, it's a win-win."
(You’ll find more advice and expert reaction below.)
Notification makes hack particularly concerning, expert warns
11:42 , Andrew GriffinThe specific nature of the notification “makes the threat considerably more convincing and potentially much more damaging”, said Marijus Briedis, chief technology officer at NordVPN. And not only because it is a concerning message in itself, but also because it could lead to yet more dangers for customers.
“This is an unusually brazen and threatening message,” he said. “The attackers aren't simply claiming to have breached ASOS - they're publicly telling the company to engage with them or they will leak what they say they have obtained.
“What makes it even more concerning is how that threat appears to have been delivered. A message apparently written for ASOS's data protection and IT teams has instead been pushed directly to customers through the company's own app notification system. That suggests someone has gained unauthorised access to at least part of ASOS's systems, although we don't yet know how extensive that access is.
“The attackers claim they have ‘fully compromised’ ASOS's Snowflake instance. Snowflake is a cloud data platform businesses use to store and analyse large quantities of information. If that claim proves genuine, the critical question will be what information was held there and whether any of it was accessed or downloaded. At this stage, however, customers shouldn't assume their personal or payment information has been stolen - that hasn't been established.
“What customers should be particularly alert to now is what happens next. High-profile cyber incidents create ideal conditions for phishing attacks. Criminals may exploit the publicity by sending emails and texts claiming to be from ASOS, perhaps asking customers to reset a password, confirm payment details, check an order or claim a refund.
“Don't click links in unexpected messages, even if they look convincing. Go directly to the ASOS app or website instead. Customers should also make sure their ASOS password is unique and, if they've used the same password elsewhere, change it on those accounts too.
“Until ASOS completes its investigation, we won't know exactly what has been accessed or how the attackers got in. But this incident shows how powerful access to a trusted communications channel can be. When an attacker can potentially speak to customers through a company's own systems, it makes the threat considerably more convincing and potentially much more damaging.”
What could happen to Asos?
11:31 , Andrew GriffinIf the worst fears about the hack are true, then Asos could face substantial punishment, says Lewis McKeown, a commercial lawyer at Square One Law.
“Should the hackers be successful in leaking the personal data of ASOS customers then the business could face devastating financial and reputational consequences,” he said.
“UK GDPR, supplemented by the Data Protection Act 2018, places obligations on businesses to maintain appropriate security measures and respond appropriately to personal data breaches.
“Where a breach is likely to pose a risk to individuals’ rights and freedoms, companies generally have to notify the Information Commissioner’s Office (ICO) without undue delay and, where possible, within 72 hours of becoming aware of it, with higher-risk breaches potentially requiring direct notification to affected customers, which we’ve already seen this morning courtesy of the alert sent out from the Asos app.
“The ICO could then investigate whether the company had appropriate technical and organisational measures in place and, depending on the circumstances, enforcement action and a significant fine may follow.
“Beyond regulatory fines, the business could also be faced with compensation claims from customers, the cost of investigating and remediating the breach and eroding customer and investor trust, as well as a damaged commercial reputation.”
Expert advises customers to check their accounts and be wary of scams
11:10 , Andrew GriffinCustomers should make sure they are protecting their accounts and beware of anything that might be a scam, warns Junade Ali, cybersecurity Expert and fellow at The Institution of Engineering and Technology. (It’s important to note that we still know very few details about the attack, including whether personal data has actually been stolen – but this is good advice whatever has happened.)
“This is yet another example of criminal hackers using data for extortion purposes,” he said. “A threat actor has essentially pushed a notification on the ASOS app threatening to leak a corporate database if ransom demands are not met.
“Typically ransomware actors will also seek to encrypt data unless a ransom is paid, but there is no evidence of that here and cybersecurity best practice to have backups to minimise the risk of this happening. Here the threat actor has chosen to make the compromise visible, which is not uncommon for extortion purposes.
“Users should take steps to ensure they are using randomly-generated, long, unique passwords for different accounts, enable Two-Factor Authentication where possible, and back up important data. Be wary of scammers who may attempt to use any personal data for scams.”
Cyber attack does not appear to have affected website or app
11:06 , Andrew GriffinAsos’s website and app appear to be functioning as usual, despite the alarming message and apparent hack. Visitors still see the usual website (including no information about the attack itself).
Share price continues to plunge
11:04 , Andrew GriffinAsos’s shares have now fallen 12.5 per cent since 10am, around the time the notification was sent. That means it has lost about £70 million in value.
This year had been something of a turnaround for ASOS, which has been troubled in recent years. It is still up around 56 per cent from where it started the year, even despite the plunge in the wake of the hack.
But the troubles nonetheless continue affect the company deeply, even before today. It has posted losses of hundreds of millions of pounds in recent years, and its shares have lost 84 per cent of their value over the last five years.
Hack is 'one of the most visible' in history, says expert as he warns users not to click on notification
10:45 , Andrew GriffinDon’t click on that notification, or follow the Telegram link that’s in it. That’s the advice from one cyber security expert.
“This has got to be one of the most visible hacks in history. The fact the hackers managed to send a push notification to customers suggests they have gained access to at least some of ASOS’s connected systems, but it doesn’t prove their full claims about the extent of the data breach. The threat actors say they have compromised the Snowflake cloud data platform, which would put a lot of customer data at risk,” said Jake Moore, global cyber security adviser at ESET.
“By broadcasting their breach directly to ASOS app users, the threat actors are likely trying to apply pressure to ASOS, showing how extensive their access is so they can leverage some sort of ransom. ASOS app users should not click on the notification and avoid the temptation to engage in the Telegram account if it was shown for them.”
'ASOS hacked' notification in full
10:39 , Andrew GriffinHere’s what the message sent to customers reads.
“Dear Asos DPO and IT, we have fully compromised the Snowflake instance,” the message, apparently written by the cyber attackers, reads. “Engage with us, or we will leak it,” it continues, before linking out to a Telegram chat.
DPO refers to the data protection officer, the appointed person in a company who takes responsibility for safeguarding customers’ information. Snowflake is an online data platform used by a wide array of companies.
What is Snowflake?
10:38 , Andrew GriffinThe notification claims that hackers have “fully compromised the Snowflake instance”. (We have no idea at the moment whether that is true: while the ability to send the notification itself suggests that cyber attackers do have access to some Asos systems, we don’t know which or how extensive their break-in is.) But what is Snowflake?
It is, in short, a data platform. It offers a cloud platform that allows its customers to store and analyse their data. As with many companies in recent times, Snowflake’s marketing particularly focuses on its AI tools, but it also offers more traditional data storage and analysis too.
It says it has more than 12,000 customers, which includes brands including the New York Stock Exchange and OpenAI. Snowflake doesn’t mention Asos on its website, but a listing suggests that it is a user of “Simon AI”, a separate product works with Snowflake and uses artificial intelligence to help with marketing.
“Instance” is a computing term for a specific and particular piece of software. In this case (and if the claims are true), it would probably refer to Asos’s data on Snowflake’s servers.
Asos share price plunges after notification
10:28 , Andrew GriffinAsos’s share price has dropped around 5 per cent in the last half hour, since the notification was sent, and it continues to fall.
What does Asos have to do?
10:26 , Andrew GriffinUK law requires British companies such as Asos to report any data breaches to officials within three days. Companies must also quickly notify any affected people, in the case of “high risk” hacks.
Hello and welcome...
10:19 , Andrew Griffin... to our live coverage of what appears to have been a major cyber attack on online shopping platform ASOS.