The owner of high-street fashion brands Hobbs and Whistles has been hit by a cyber attack, marking the second hack on a UK retailer in the space of a week.
South African retail group The Foschini Group (TFG) said it became aware of the “cybersecurity incident” on Sunday, affecting its UK subsidiary TFG London, with “certain of its IT systems” impacted – specifically its Phase Eight, Hobbs and Whistles brands.
But it said there is “no reason to believe that payment information is at risk”.
Other high street brands, including Inside Story and White Stuff, are not affected.
TFG said it had reported the incident to the relevant UK authorities.
The group added that its operations in TFG Africa and TFG Australia were not affected.
TFG London said: “On Sunday, 11 October, TFG London identified a cybersecurity incident affecting some of our IT systems, specifically impacting our Phase Eight, Hobbs, and Whistles brands.
“We are actively investigating and working with external cybersecurity specialists.
“Stores are open as normal, but some of our brands’ website capabilities may not be available as the investigation continues.
“We apologise for any disruption and will provide additional updates to our customers as appropriate.”
Customers who placed an order with Phase Eight, Hobbs or Whistles before Sunday were told their purchase would be processed and delivered as normal.
TFG London said there could be delays in orders placed after Sunday, but added there was no need to resubmit anything.
The subsidiary said returns could be made in store, adding it was working on a solution for postal returns and would keep customers informed.
TFG London first entered the UK market in 2015 after buying Phase Eight, and has since added womenswear brands Whistles and Hobbs, homeware brand Inside Story and lifestyle brand White Stuff to its portfolio. Headquartered in London, the subsidiary counts more than 3,000 employees and operates across the UK, Europe, America and Asia.
The attack on TFG London comes a week after fast fashion business Asos said an “unauthorised party” had gained access to some personal data, including names and contact details.
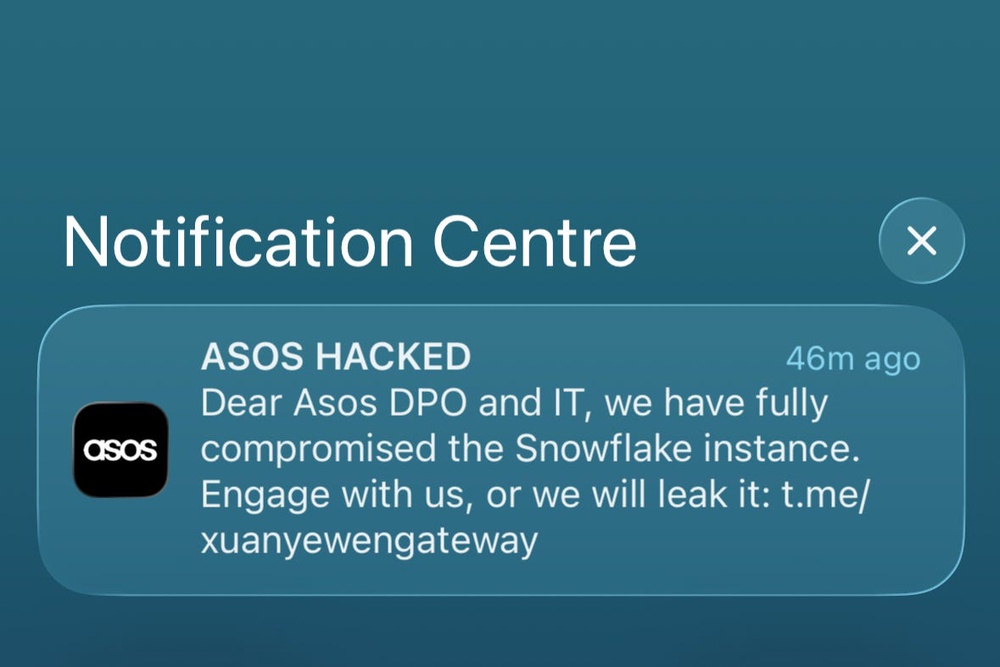
Asos customers received a phone alert saying that the retailer had been hacked, which claimed the data storage firm Snowflake had been compromised.
Snowflake later said the breach was not caused by a vulnerability or flaw with its platform.
On Monday, it was reported that H&M was investigating claims it was targeted by a cybercriminal last week.
The Swedish fashion giant said it was looking into a potential cybersecurity incident carried out by a group called ShinyHunters, The Times reported.
Jackie Wadhwa, head of cybersecurity at Digital Envoy, said the latest attack “highlights the growing cybersecurity risks facing the retail sector”.
“With the rise of increasingly sophisticated, AI-powered attacks, it is likely that we will continue to see retailers targeted by cybercriminals looking to exploit vulnerabilities in security processes and systems,” she said.
Ms Wadhwa said e-commerce businesses “typically rely on frequent touch points and proactive communication with their customers”.
“This model means a higher exposure to attacks if cybercriminals compromise customer environments, with the potential for customers and their data to be used as leverage to extort businesses.”
Read MoreSpain's king and queen to visit Ceuta as territory grapples with protracted migration crisis
Naturally occurring fungus could help protect wheat from disease – study
Poland blames Starlink sabotage on Russia
Investigation launched after man found dead in custody at troubled Met Police station
What is XFG Covid strain? Symptoms to look out for as UK cases rise
Sir Ranulph Fiennes stepson says explorer is ‘very lonely’ and calls for visits